Showing posts with label network security. Show all posts

Friday, November 10, 2023

When It Comes to Computer Networks, Trust No One and No Thing

By: John Shepler

Network security is a major headache for business. It almost makes one long for the days of one computer per desk and nothing connected to anything else.

Almost. Those air-gapped computers weren’t all that secure either. Sneaker networks, meaning running around with floppy discs, allowed malware to spread and sensitive files to be copied. It’s just that today’s networks with LANs, local data centers, multi-clouds, and the Internet make it really hard to know who’s sneaking in where and what they are up to.

One breach in a corporate network can run up a cost in the millions. If ransomware is involved, the bill can be a lot higher… and a lot more disruptive. What can you do? Don’t be so trustful. Make sure your system is suspicious of everybody and everything all the time. The buzzword for that is “zero trust security.”
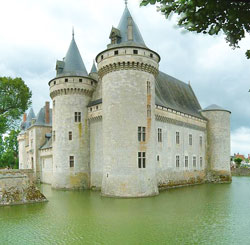
Protect your castle with better network securityWhat is Zero Trust and How is it Different?
Traditional network security is sometimes compared to a castle with a moat. The castle is your corporate network. Everybody inside the castle is considered to be friendly and trustworthy. Everybody beyond that moat is suspected to be an enemy. The drawbridge is your firewall. It works to keep the bad actors away from the castle while allowing trustworthy visitors access. It assumes that everything bad is going to come through the Internet.

There are a couple of weak links with this approach. First is that some bad actors can already be inside the castle. There are spies and infiltrators and even trusted employees that have turned rogue. Of course we want to trust our colleagues, and that’s how we get in trouble. Even worse when we automatically trust our vendors and customers.

Then there is the famous tale of the Trojan Horse. Gee, it sure looks safe enough. Let’s open the firewall and bring it in. You can just imagine some well-meaning but naive individual in your company doing just that. Of course the gullible Trojans got the worst of that deal since once the Greeks were inside they had the run of the city.

Moral of the story: It’s too easy to have your organization destroyed by one little misstep. Trust no one and no thing. Network security is not an insult to your integrity. It’s a way to make everyone more secure and prevent little slips from becoming major disasters. That means high security processes both inside and outside the network.

What Makes Zero Trust Work?
It starts with having everybody and every thing, meaning anything attached to the network, prove that it is approved for access and what they are approved for. You can’t really say that because someone has been cleared by, say, logging-on, that they should be able to access all the files and every peripheral on the net.

Oh, no. You must have a need to know for everything you want to access. That leads to segmenting the network into much small pieces that each have to be accessed separately. You may have access to one set of information to be able to do your job, but no way are you getting into some of the companies trade secrets or even financial data. Access to HR files? Fat chance… unless you are specifically authorized to see them.

Each use and each device will have a profile constructed that says what they can do and where they can do it. These lists will be used by the network administration to grant or refuse access. You may find that your access times out and you have to log in again to keep using a particular resource. Multi-Factor Authentication, like password plus a code sent to a mobile phone or a hardware key that must be plugged-in, is especially valuable for access through the Internet or to highly sensitive data.

Zero Trust Security does take some doing to implement and maintain, but it can also be the means that keeps hackers and scammers of all sorts from stealing your information or damaging your systems. Are you feeling vulnerable? Learn more about how to secure and safeguard your network and get a complementary quote appropriate for your business.
Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter


Wednesday, September 11, 2019

You Need a Black Cloud Software Defined Perimeter

By: John Shepler

Secure your network with black cloud SoftwareAre you a trusting person? Too bad. That’s going to get you hacked. Respect and privacy are admirable things, but they are not guaranteed by today’s Internet. In addition to all the incredible employees, partners, suppliers and customers that you hold in high regard, there is a dark underbelly of professional criminals, hobbyist & mercenary hackers, mischief makers, psychotics, and nation states with agendas all trolling the same network. Some are looking for victims of opportunity. Others have you in mind as a target. Can your firewall and VPN fend them off?

The Virtual Hopefully Private Network Connection
The VPN or Virtual Private Network was designed to make the Internet act more like a private line or MPLS (Multi-Protocol Label Switching) network. Even if you have a T1, DS3, OC3 or Ethernet private line at the office, you have a big security hole when an employee out on a sales or repair call stops by the coffee shop and connects back using the free Wi-Fi provided by the store.

Free really means free and open. That guy in the corner staring at his laptop is watching your traffic. He either hacked the shop’s WiFi or created his own look-alike “free” WiFi network that you connected to instead of the real one. This is called “man in the middle” and it is what VPN was designed to protect against. The VPN creates an encrypted connection called a “tunnel” from your employee’s computer to your office server. That makes it pretty hard for someone to get in the middle of the conversation unless they have the private key… and they don’t.

VPN Weaknesses
Not all VPNs have a rugged 256 bit military-grade encryption. Some use protocols that are relatively easy to crack with available hacker tools. PPTP (Peer to Peer tunneling Protocol) is over 20 years old and is desirable because it is fast and easy to setup and use. It’s also more vulnerable than protocols with stronger encryption.

Not all VPN vendors are equally capable. Weak ones may have back doors in their servers or other weaknesses that make it easy to hack the VPN server in the cloud and get everybody’s data. You won’t know until you are hacked and can’t figure out how.

An overall weakness of VPN is that it just protects the tunnel into your company. If that is compromised one way or the other, your entire network and everything on it is wide open to explore and perhaps attack. it would be better if only a small part of the company assets were exposed instead of everything all at once.

The Software Defined Perimeter Black Cloud
The idea behind a Software Defined Perimeter (SDP) is that trust is minimized by allowing access to resources user by user on a need to know basis. The research was done by the U.S. Department Information Systems Agency (DISA) and has come to be known as a “Black Cloud.” The black designation means that the network infrastructure is hidden within the cloud. There are no visible DNS or IP addresses.

SDP authenticates each user and only gives them access to the resources you have approved for that particular user so they can do their jobs. The user or IoT device has no idea what else is on the network. They can’t see it. If they can’t see it, they can’t get access. Someone impersonating that user can’t either.

A system of SDP Hosts and Controllers communicate and verify the authorizations. The Controller has the job of connecting the Initiating and Accepting Host data channels through a Gateway, once authentication and authorization has been completed through the control channels.

The SDP is not only between clients and the data center. It is also deployed within the data center to partition the network to isolate high-value applications. Only a limited number of users with have access to the highly protected application or even know it exists.

Encryption and cloaking are key to SDP security. The usual network probing, such as port scanning, won’t work because nothing will show up in the scan. In a way, SDP is creating virtual networks on a user by user, session by session, basis. What goes on behind the curtain is a complete mystery.

The End of Networks As We Know Them?
The TCP/IP network that has served us so well for decades has to go underground to keep its relevance in today’s high threat environment. We can no longer do business without the Internet and there are just too many bad actors on the public Internet. Technology must evolve to provide the illusion of a simple open Internet but with none of the familiar network topology visible.

Has your company network been hacked or are you concerned about the business disruption this might cause? Right now would be a good time to see what advances have been made in network security, especially managed security solutions in the cloud.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, February 03, 2014

How You Can Benefit From Wavelength Services

By: John Shepler

What do you do when you have a need for high bandwidth, security and flexibility in your WAN connections? This may be the time to take a closer look at wavelength services.


What tradeoffs should you do to ensure that you’re getting the right bandwidth for your operation? Certainly, there is the protocol competition between the dedicated point to point line services provided by SONET/SDH and Ethernet over Fiber. Both will get your packets from point A to point B, but you may find that locations lit for EoF have access to much higher bandwidths for the same lease price or a cost savings if you don’t need a BW upgrade.

One important consideration is the protocol that you wish to transport. Ethernet is easiest to connect and most efficient over Ethernet WAN services. SONET/SDH is designed for TDM, but can also support packet switched networks. The waters have been muddied lately by the addition of Ethernet over SONET that gives you Ethernet services running on mature SONET fiber optic networks.

Another tradeoff worth doing is lit fiber vs dark fiber. Wavelengths are a lit fiber service. They are fully managed in the sense that the carrier provides the fiber path plus the terminal equipment that accepts and delivers your traffic. You don’t need to be concerned about the inner workings of the network because the carrier takes care of that for you.

The big advantages of dark fiber are improved security, since you are providing the terminal equipment at each end of the fiber, and the ability to create your own wavelengths. You’ll need to invest in the CWDM (Coarse Wavelength Division Multiplexing) or DWDM (Dense Wavelength Division Multiplexing) equipment. By doing that, you can have as many wavelengths as you wish, each running a different protocol. You can even multiplex wavelengths to create higher bandwidth pipes.

What is the right connectivity solution for your needs? Get expert recommendations on fiber optic wavelength services now.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, August 12, 2013

Big Data Makes Big Push For 100 Gigabit Bandwidth

By: John Shepler

Just a few years ago the notion that businesses and government agencies needed 100 Gbps WAN bandwidth seemed absurd. Why, the provider’s core networks ran mostly at 10 Gbps, with some moving to 40 Gbps to handle high traffic levels from many simultaneous customers. Today, those same customers are expecting their service providers to give them the option of 40 Gbps and even 100 Gbps connectivity.

Find the bandwidth you need for maximum productivity...What could be causing this massive increase in bandwidth requirements? Two words: Big data. Big Data offers big opportunities to enhance business processes and mine databases, but it consumes big processing, big storage and big bandwidth. Big storage and big processing have been the focus of cloud computing providers as well as data center expansions. Big bandwidth is now the last piece of the puzzle to be put in place to create an integrated solution.

Where is all this bandwidth going? Some of it goes to interconnecting multiple business locations. Other connections go to remote data centers for disaster backup and recovery. Some is needed to communicate with customers and suppliers. In the case of content producers, large amounts of bandwidth are needed to transport that content to the local service providers, like cable companies, or directly to the end user. The latest wrinkle is the rapid rise of cloud computing solutions. Putting those cloud resources to best use is proving to require massive increases in bandwidth.

The reason that cloud computing needs big bandwidth is that most of the traffic that used to be carried on the LAN now needs to be carried through the WAN. The enterprise data center with all its processors and disk drives is generally located in proximity to the users so that the organization can have control of the network connections. This has the dual benefit of minimizing costs because there are no traffic fees and increasing security because the entire network is under local control.

The cloud changes this equation. Processing and storage is moved to a remote data center and most of the local data center facilities go dark. The local network still connects all of the PCs, printers, SIP telephones, switches, routers and other devices. Some servers may still stay local. But the big data processing is done elsewhere where there are enough compute resources to crunch all that big data into more bite size pieces. The issue is how to get all that data to and from the cloud.

What happens when you skimp on WAN bandwidth? The cloud keeps running at full speed, but its inputs and outputs slow to a crawl. Think of a WAN connection as a pipe, as it is sometimes called, and you can visualize how too small of a pipe keeps the flow (of data) at a trickle. The local experience is that the system isn’t very responsive and interactions can become unpredictable. There can be big congestion delays where nothing happens on the screen for long periods of time. What’s worse, you don’t know if you’ll have a result in half a second, half a minute or who knows how long? That’s a productivity killer if there ever was one.

People to cloud communications is critical for high employee productivity, but machine to machine communications can be more important. It’s the machines that generate data at a rate humans can’t possibly equal. Those machines might be data banks, sensors, machine tools, video cameras & displays, server farms and so on. What’s important is that they are not constrained by the capacity of the communication channel.

tw telecom is one of the latest carriers to announce that it has introduced 40 Gbps and 100 Gbps business Ethernet services in the 75 metro markets that it serves. These services are in addition to the 2.5 and 10 Gbps bandwidth options that have been in place for some time. Traditional fiber optic technology offers up to 10 Gbps on a single fiber strand or one of several wavelengths that share that strand. Bonding multiple wavelengths using DWDM (Dense Wavelength Division Multiplexing) increases that carrying capacity up to 40 or 100 Gbps with a single connection to the user.

Who needs 100 Gbps bandwidth? Right now it’s only the largest corporations, financial institution, research labs or government agencies. But how long ago was it that DS3 at 45 Mbps was considered big bandwidth and OC-3 entry level fiber at 155 Mbps was plenty for most enterprises? Today 100 Gbps is on the cutting edge of technology. Tomorrow that level might be considered par for the course or even entry level for many businesses.

Would your organization’s productivity benefit from a bandwidth increase? You may not need anywhere near 100 Gbps, but you should know that fiber options from 10 Mbps to 1 Gbps are readily available and more affordable that you imaging. Get fiber optic bandwidth options available for your business locations.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, December 03, 2012

Cloud Computing Appropriate For Small Business

Cloud computing is all the rage among medium and larger enterprises. You might say that there is a veritable stampede from local data centers to cloud based services. Small businesses may be left scratching their heads trying to figure out if the cloud makes any sense for them or if it is simply overkill for their size organizations.

Cloud services designed with the small business in mind...In reality, cloud computing may make even more sense for smaller companies that it does for large ones. Why? It’s because major corporations have major budgets for large IT staffs and in-house data centers. The idea is that if you integrate everything under your control, you’ll logically have the lowest costs, greatest security and fastest response times.

There are many cloud examples that prove this is obsolete reasoning. Hiring a specialist service, the cloud, can actually lower your costs, improve security and allow you to react to changes in business conditions much faster than doing it all yourself.

For smaller businesses, the cloud may well become your IT department or an adjunct to a consultant that works on a less than full time basis. Cloud service providers have the expertise in-house that you can’t really afford. This means that you can get top-notch support by people who are trained in the state of the art included as part of your monthly fee.

Let’s take a look at typical cloud computing solutions that are appropriate for small businesses. One service that nearly every business, including SOHO (Small Office, Home Office), is embracing is cloud backup storage. The value in remote backups is that even if your local office is wiped out by fire, flood or tornado, your business records remain safely intact. Storage tends to be very affordable and more cost effective than buying more and more stand alone disk drives. The beauty of the cloud is that you don’t have to worry about filling up the next disk drive. Storage is virtualized and nearly unlimited.

An extension of online storage is backup and disaster recovery. These systems give you an easy to use control panel so that you can figure out what files to bring back down when needed. One thing to remember about online backup is that the limiting factor to how fast you can upload and download is the speed of your bandwidth connection. It’s not much of a problem on upload because files are being transmitted in the background as you work. Only a little bit of data needs to be sent to the cloud every hour.

The real limitation is when your entire office or local file storage is wiped out. You’ll be glad you have backup storage in the cloud so you can stay in business, but it can take days or weeks to bring everything back down. You’ll need to pick and choose which files are most important to continuing business and get those back first. The rest can be restored as a background activity.

Some cloud solutions get around this by having mirrored storage in both the cloud and in a secure appliance located in your office. This makes it really easy and fast to get a file you may have accidentally deleted and fast to restore an entire system because so much of the data is local. Of course, if the disaster is extensive and all of your on-site equipment is destroyed, you’ll still need to get everything back from the cloud.

By the way, a big advantage of cloud solutions is that you can be quickly back in business at another location. This is especially true if some or all of your connectivity is via the Internet. Set up shop at home, a temporary rental office or at the local coffee shop. As long as you have bandwidth, you’re in business.

Web servers are another technology that makes sense in the cloud. Many companies already rent shared or dedicated server space from companies that specialize in selling these plans. There is no need for anything more sophisticated unless you have the type of business with such variations traffic that you wind up paying to support the maximum number of visitors possible. Cloud servers can be scaled up and down almost instantly. You pay only for what you need right now and add more capacity during the holiday season or other high traffic times.

The old fashioned way to get the computer tools you need for your business is to buy software packages and then spend some time maintaining and upgrading them over the years. The new approach is called SaaS or Software as a Service. The actual software resides on a cloud computing platform remotely. You use the office systems or specialized software by connecting to the cloud. The cloud provider takes care of patching and upgrading the system so you have no maintenance headaches and no need to invest in expensive software. Once again, you pay for how much you use by the month.

Security is now moving to the cloud. The truth is that few businesses have security experts on staff and the attacks are getting bolder and more sophisticated. A simple anti-virus program may no longer be enough to prevent an intrusion or shutdown of your business. The way to have the latest network security is to buy a cloud based solution that acts as a firewall between your business and any potential trouble makers. Like software, security as a service is maintained by experts who have nothing else to do but stay on top of threats.

Finally, even your telephone service may make more sense in the cloud. Hosted PBX or Hosted VoIP systems move all the call switching to a cloud service provider that also makes the connection to the public phone system. All you have at your location is IP telephones and perhaps a specialized gateway device. You pay by the phone by the month and some providers even include new business phones as part of the deal at no extra cost.

Is it time to reconsider the costs and performance of the IT systems used in your small business? There are great deals to be had that can help you avoid investments, lower expenses and keep up with the latest technology. Get competitive quotes from cloud computing providers and see what works best for your company.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, October 01, 2012

Secure To The Core Cloud Hosting

Moving to cloud based solutions is making sense for more and more companies. The cloud offers easy scalability, near-infinite resources, high performance, no maintenance headaches and the opportunity to avoid capital investments and pay only for what you use. The one nagging issue is how secure is the cloud, really?

Move up to highly secure cloud and network services.MegaPath, a major player in private networking and hosted IT services, has taken a big step toward assuring businesses that their data and business process will remain private by introducing a concept it calls “secure to the core.” Just what does secure to the core mean and how can it work for your business?

Nearly every cloud service provider touts its security. This generally centers around the data center itself. Many are SAS 70 Type II and SSAE 16 compliant with physical security that include biometric scanning, a full time security staff, video surveillance and a walled fortress. Inside there are redundant power and cooling systems, fire suppression and multiple WAN connections to the outside world. However, this last group is really more about reliability than security.

With proper personnel screening and all the physical and technical barriers to entry, it’s not that hard to physically keep people out who don’t belong in the data center. It’s more difficult to keep them out when they come in through the Internet.

The Internet is a weak link when it comes to any data security program. The most motivated and talented of wrong-doers operate in this domain. They eagerly stalk potential targets to penetrate and make off with intellectual property, credit card numbers, personal data that can be used for identity theft and anything else of value. It takes talented network security people and an array of firewalls and security appliances to protect high value business, organizational and government assets that face the Internet.

This is where MegaPath has a leg-up on a lot of cloud service providers. They also have the latest in high security data centers that meet stringent industry compliance standards. What MegaPath has that most providers don’t is a large private network completely independent of the Internet.

When you think about it, companies with multiple locations or Intranets that include key suppliers and customers don’t really need the Internet for internal communications. In fact, it is highly desirable to keep internal communications on a private network for both security and performance. MegaPath makes this affordable for all size businesses through their nationwide MPLS (Multi-Protocol Label Switching) fiber optic network. The label switching technology of MPLS makes packet forwarding simple and efficient. It also allows customers to chose from eight levels of QoS (Quality of Service) so that time sensitive packet streams get the priority they need to maintain integrity end to end. This is ideal for enterprise VoIP telephone systems and video conference or telepresence.

MegaPath can offer you MPLS network connections throughout the United States plus Managed SSL VPN, Retail Access SSL and Business Continuity SSL. Their compliance services help companies meet regulatory requirements such as PCI DSS, FFIEC/NCUA, HIPAA/HITECH, GLBA and SOX.

Of course, you probably want Internet connections as well to serve the general public and commercial buyers, and for employee access to the vast information resources available worldwide. MegaPath offers a comprehensive security array called UTM or Unified Threat Management. This includes advanced firewall, intrusion prevention, anti-virus protection, Web filtering, anti-spam, Web application control and data loss protection. These UTM services can be implemented within the cloud, at the customer’s premises or in a hybrid configuration.

Are you looking for cloud services that have rigorous physical and network security protections? Get features and pricing for secure network and cloud services from MegaPath and other high quality providers.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Tuesday, June 26, 2012

Why Colocate To An Omaha Data Center

When big companies think of colocation data centers, they’re probably thinking of 60 Hudson St in New York City or One Wilshire in Los Angeles, California. Where else should they be thinking? Why, Omaha, Nebraska, of course.

Consider Omaha, Nebraska for your next data center colocation....Omaha? What’s in Omaha? Well, billionaire Warren Buffett, the “Oracle of Omaha”, and his legendary Berkshire Hathaway conglomerate holding company. That’s just one of five Fortune 500 companies headquartered in Omaha. In fact, Forbes magazine has called Omaha the nation’s number one “Best-Bang-For-The-Buck City.” More to the data center point, Omaha is home to the Scott Data Center complex.

Scott Data Center offers over 110,000 square feet of data storage facilities. It has been continually operating since 2006 and is currently just one of two multi-tenant data centers in the United States to achieve Tier III Certification for both design and construction. This certification was awarded by the Uptime Institute, an industry organization focused on improving data center performance and efficiency. They award tier certifications in 26 different countries. Tier III facilities support critical business applications.

One of the newest tenants is Level 3 Communications, the worldwide telecommunications carrier for voice, data, and video. Level 3 is deploying a new enterprise-grade data center within the Scott Data Center complex. It will join more than 350 Level 3 data center facilities in North America, Europe and Latin America. You can select the level of service you require, including the Premier Elite facilities, such as the new Level 3 Omaha data center. All of these data centers are connected via Level 3’s 165,000 intercity, metro and subsea fiber route miles that provide low latency access to corporate assets around the world.

But, still, why Omaha? The fact that Omaha is located in the center of the United States is an asset when it comes to disaster prevention and recovery. If you are insistent on avoiding a situation that wipes out your headquarters building and takes all of your IT facilities with it, you need redundant data centers that are geographically diverse. Keeping everything in one building is efficient, but it is risky for floods, tornadoes, hurricanes, earthquakes and fires. A separate facility across town is one step better. A facility someplace else in the country that doesn’t have the same risks is better yet.

Omaha isn’t subject to earthquakes and certainly not likely to be a victim of any coastal tsunamis. The Scott Data center design protects it from any potential seismic activity. It is elevated out of the flood plain to avoid any issues with an overflowing Missouri River. Yes, tornadoes can be an issue in the MidWest, but the Scott facility can withstand 250+ mph winds and the uplift of tornado level winds.

There are also financial advantages to locating in Omaha. Electrical power is available and costs well below the national average. You know that data centers are power intensive, both for equipment operation and cooling. There are also pricing and tax incentives that make Omaha an attractive place to build an expensive and sophisticated facility like a data center.

By the way, Scott Data Center meets the security requirements of the Department of Defense. That includes a 24/7 security desk, gated perimeter, dual authentication, surveillance cameras, barrier wall, man-traps, biometrics, generator backup and redundant cooling. Think your equipment and data will be safe? You think right.

Are you thinking about relocating your data center or establishing a complementary or alternative colocation facility to current coastal locations? Get features and pricing on colocation data center facilities available in Omaha and nationwide to meet your business needs.

Click to check pricing and features or get support from a Telarus product specialist.


Photo of Omaha skyline courtesy of Wikimedia Commons.


Follow Telexplainer on Twitter

Friday, November 18, 2011

Cloud Hosting Providers For Converged Networks

Cloud computing services are growing geometrically. If you haven’t gotten on-board yet, it’s probably because you aren’t convinced of the cost savings, security or the ability of the cloud to cover all bases for your IT needs. That picture is changing rapidly. Let’s take a snapshot of what’s available now for SMB users.

Cloud hosting providers have many services to meet your business needs...When we think of cloud computing, the picture that comes to mind is one of a giant brain in the sky that runs operations for hundreds or thousands of companies. That’s the approach that gets all the press, but it’s far from the entirety of the market. Indeed, there are many other providers out there who can deliver the virtual services you need on a less grand scale. You may not be able to get everything from one service provider, but the building blocks are out there to handle your voice and data needs.

That’s important, because enterprise VoIP solutions are driving a trend toward converged networks. If you only consider moving traditional data center servers to the cloud, you’ll be missing a big piece of the puzzle. The other trend that’s important is fixed mobile convergence that integrates cell phones into your telecom infrastructure. Mobility can be the link that makes or breaks your productivity in the future.

The foundation of cloud computing is cloud hosting that incorporates Infrastructure as a Service (IaaS), Platform as a Service (PaaS) and Software as a Service (SaaS). Cloud infrastructure is virtualization on steroids. IT departments have found that virtualizing servers ups the efficiency of the physical server hardware. What cloud computing does is greatly expand the virtualization to include huge racks of high performance servers plus storage and bandwidth. It differs from the virtualization that you would do yourself or the virtual servers you’d rent from a colocation center in that it is sold incrementally on-demand. You pay by the minute, by the hour or by the number of CPU cycles used.

Another characteristic of cloud hosting is that it is highly elastic or scalable. If you start to run out of capacity, you simply order up more virtual servers. The cloud operating system takes care of how these resources work in concert to provide the capacity you need. At no point do you have to purchase, install or maintain any equipment. The cloud service provider takes care of this with a 24/7 technical staff.

There are actually three types of clouds to choose from. The one that first comes to mind is the public cloud that serves many users simultaneously. You gain access via a private line or dedicated Internet service. Companies that have highly sensitive applications, unique requirements or simply want more control go with a private cloud. That is a similar infrastructure to the public cloud but on a scale suitable for one company. The hybrid cloud is a combination of the two. Public facing or non-critical applications run on the public cloud, while a separate private cloud handles very sensitive applications.

While cloud computing is thought of a data processing service, there is also a voice cloud known as cloud communications or hosted PBX. In this case, the computing resources are specific to telephony needs and the connectivity is by SIP trunk from your location and to the public switched telephone network from the provider. You no longer need a PBX phone system in-house or any telephone trunk lines. What you have is SIP telephones connected to your network and a converged SIP trunk from your business location or locations to the service provider. Some hosted PBX systems integrate cell phones into the system so that you have the same capabilities while mobile as at your desk.

Some of the cloud services you can readily get include cloud hosting, hosted PBX, unified communications, enterprise cloud security, private/public clouds, cloud storage, hosted Exchange, SharePoint, disaster recovery, anti-spam and anti-virus, hosted firewalls, and dedicated cloud access connections.

Are you feeling that you may be missing out on productivity improvements, cost savings, agility of scaling your business, or advanced features available in the cloud? This would be a good time to explore options with multiple cloud hosting providers. You can start small and grow or make a step-change relocation to the cloud, depending on what works best for your company.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, October 24, 2011

IP WAN over MPLS Advantages

When we think of IP wide area networks, the first thing that comes to mind is the Internet. While the Internet does have almost universal connectivity and modest cost to access, there are some serious issues when it comes to business applications. Bandwidth, latency, jitter and packet loss have no guarantees and few expectations. Security is a joke. But aren’t other methods to interconnect business locations costly and hard to manage?

It is possible to set up a private IP network that lets you use your familiar IP addressing schemes and avoid encryption, firewalls, tunnels, and additional hardware. You’ll gain a performance advantage compared to using VPN techniques over the Internet and save yourself the administrative headaches of trying to manage a WAN with inherently indeterminate characteristics. Who offers something like this? It’s TelePacific, one of the nation’s largest competitive carriers.

TelePacific’s 1Net is an IP VPN running on a private MPLS network, not the Internet. Since MPLS or Multi-Protocol Label Switching can transport almost any protocol, it can be set up to mimic the Internet while keeping your data private. Only the locations that you set up can exchange traffic. No one outside of your user group can capture or view your data. You’ll have any to any connectivity within the group with security sufficient to address HIPPA or similar government regulations.

In fact, TelePacific set up just such a private IP Network for a medical imaging organization with 6 locations. They use it to transport patients’ private medical records among their location. Referring physicians can access patient imaging results within hours at their own computers. The system is also used for claims processing, patient scheduling and registration. Interestingly, this system also allows dedicated Internet access through a single firewall at corporate headquarters.

The TelePacific 1Net IP VPN has both cost and performance advantages over other secure networking solutions, including private line, ATM and Frame Relay. You can specify up to six different Classes of Service (CoS) to support sensitive real-time services such as VoIP telephone and teleconferencing. On Net, latency for all CoS is specified at 50 msec. That rises to just 100 msec for extended reach locations off the TelePacific network but still within the US. Network availability is 99.999% (5 nines) both on and off network locations.

The Classes of Service are CoS 1 for VoIP real time traffic, CoS2 for video conferencing and real time data traffic, CoS3 for high priority, delay sensitive business data like Ecommerce and Citrix, CoS4 for medium priority delay-sensisitive business data such as CRM and WebEx, CoS5 for general less delay sensitive business data like ERP, and CoS6 for best effort traffic with no prioritization. That’s typically Email and FTP.

Are you cringing at the cost and effort involved in linking your business locations by private lines or frustrated by the highly variable performance and difficulty in securing the Internet? Perhaps the best solution for your business needs is a private IP VPN based on MPLS networking. Check prices and features to compare with your other choices.

Click to check pricing and features or get support from a Telarus product specialist.


Note: MPLS network diagram courtesy of Wikimedia Commons.


Follow Telexplainer on Twitter

Wednesday, October 19, 2011

Types of VPN Connections

Virtual private networking is heavily used in business. In fact, you probably have used a VPN connection today without even realizing it. It’s not a belt and suspenders service anymore. VPN connections are absolutely essential to prevent being robbed blind.

Virtual Private Networking provides security at a reasonable cost...First, let’s take a look at private vs virtually private networks. Your hardwired LAN is a private network. It would take some real effort and a lot of risk for someone to tap into your network wiring and install a device to capture traffic. The same is true if you establish a wide area network or WAN using point to point private lines. A PTP T1 line falls into that category. While it is not impossible to sneak into your wiring closet or even the telephone company and put a tap on the line, it is so difficult that only those with the most secure requirements will go to extremes to protect against this type of attack.

What distinguishes a private network is that 100% of the traffic is yours and yours alone. You are not sharing the lines with anyone else. The advantage to a private network is inherent security. The disadvantage is cost. You pay for all the construction, maintenance and monthly lease fees. It’s unlikely that your private network will be fully loaded at all times. Whatever capacity is unused goes to waste.

Contrast the private network with a public network like the Internet. They are polar opposites. The Internet allows anyone and everyone access by design. Traffic on the Internet is everybody in the pool. Your packets are intermingled with everyone else’s. Even so, a wired connection to the Internet isn’t the worst situation. That belongs to the unsecured wireless network. No need to plant malware in someone’s computer when everything they are doing is perfectly visible on any WiFi enabled computer within range. You are most vulnerable reading private unencrypted emails in a popular public hotspot. Anyone with a laptop computer and some easy to obtain spyware can be reading your messages right along with you.

It seems like such a crying shame that the one network that any employee can access at home or while traveling is such a security nightmare. That’s where the technique of encryption becomes valuable. It doesn’t matter if someone is monitoring your traffic if all they see is gibberish. You encrypt your message at one end and decrypt it at the other end and you have a created what is known as a secure tunnel through the Internet. The public network has now become a virtually private network. It’s not a private network because you are still sharing the transport with many others. It’s virtually private because no one can read your traffic and make any sense out of it.

There are two popular methods of creating Internet or IP VPNs. One is IPsec or Internet Protocol security. The other is SSL or Secure Socket Layers. IPsec is based on software installed in both the company server and the client computer. IPsec encrypts and decrypts each packet, so once you have it installed you have a virtually private line to the company no matter where you hooked to the Internet. Of course, you need to use the specific laptop or other computer set up to work with this system. You can’t just go to any computer and connect back to headquarters.

If you want to do that, you need SSL (Secure Socket Layer). The beauty of SSL is that the software is already built into Web browsers and some email programs. SSL has been popularized for ecommerce and online banking. When you go to a SSL enabled webpage, you’ll notice that the http:// has become https:// The “s” means secure page. To access it you need a user account ID and a password at a minimum. Some sites go further and ask personal challenge questions or display special graphics that give you confidence you are logged into the correct site.

For corporate wide area networks, an alternative to private lines is the MPLS network. These are multi-tenant networks that spread the cost of building and running the system among many users. MPLS networks are considered VPNs because they use a proprietary label switching protocol that isn’t compatible with IP tools. This unique protocol plus access controlled to a limited number of business clients and not the general public give MPLS networks an enhanced level of security.

Do you need private or virtually private network connects to conduct business? If so, compare VPN options and prices to help decide which mix of network techniques is right for your company.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, July 11, 2011

Advantages of SSL VPN

Computer security is in the back, if not the front, of every Internet user’s mind right now. Hacking, security breaches, identity theft and malicious bots are terms that show up in national news reports as well as user forums. Everything moving to the cloud is adding to the anxiety of anyone who has sensitive data and wants to keep it personal and private. Little wonder the interest in virtual private networks is greater than ever before.

Consider SSL VPN as an easy way to establish secure connections with your customers...What is a virtual private network and why would you want that instead of an actual private network?

The answer revolves around our desire for universal connectivity. Most companies started connecting to other locations using private line services, such as T1, DS3 and OC3. These are point to point connections that are reserved for your private use. Only you and the network operators have access to those wires and the data they are transporting. It’s fairly difficult for third parties to tap a private line and examine the packets moving back and forth.

Private lines are defined as private, but that’s not really good enough for high risk companies such as banks and brokerages. To thwart even the most dedicated line “tapper,” they encrypted their data to ensure it stayed private. Encryption is a process that takes plain text and jumbles it in such a way that it appears to be indecipherable nonsense to anyone looking. At the far end of the link, the text is decrypted and returns to its original form.

Private lines are great for communicating within organizations or with a select few suppliers, vendors, consultants and so on. But what if you want to interact with the public at large? For that you need a public, not a private, network. That’s exactly what the Internet was created to do.

The advantage of the Internet is that it connects to nearly every place and every person on Earth. That’s also its weakness. The same universal connectivity that makes it easy for billions of potential customers to reach your website makes it equally easy to do mischief or outright crime. If there was only a way to make the connection between you and your customer secure while still using the public Internet.

That solution is called the VPN or Virtual Private Network. A public network connection can be made virtually private by encrypting the packets that travel between two locations. Your particular stream of traffic is scrambled while the rest of the traffic flowing through the same network connections could be transmitted in the clear.

SSL or Secure Socket Layer is a popular technique to provide the encryption between source and destination. What makes it so popular is that SSL is supported by all modern Web browsers and many other programs, such as Email clients. There is no need to buy or configure separate encryption software used in other VPN approaches.

Anyone with an Internet connection and browser can connect securely to any site that supports SSL. The resulting connection can be called a SSL VPN. It only persists for the length of the session, but can be established at any time. You know that you are on a secure link because the address starts with https: rather than http: The “s” means secure.

Adding SSL to a site involves buying a digital certificate from a trusted certificate authority. That certificate attests to the fact that the site in question is who it says it is and not some impostor. The secure site presents the certificate to the client to prove legitimacy. It may also ask the user for authentication, such as user ID and password, to prove that the user is also legitimate.

What sites use SSL? Most any site handling financial transactions, such as banks, online stores that accept credit cards, webmail providers, cloud storage providers, remote access services, most sites that store personal data and require user logins, and businesses using the Internet to connect remote locations and home workers.

Do you need to provide secure connections for your business? If so, look into the costs and features of Affordable Virtual Private Network solutions. One or more may be just right for your particular needs.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Wednesday, June 22, 2011

Why Demand a SAS 70 Type II Data Center?

If you are considering a move to the cloud or colocation center, you want to be sure that you are dealing with a high quality operation that has the controls in place to ensure the privacy and security of your data. If you are in certain industries, such as health care and financial services, you may well be required to use this type of facility.

Check that the data center you are intersted in offers SAS 70 Type II compliance.SAS 70 is about a very structured audit into the operations of a company that handles customers’ data. It’s done to a standard developed by the American Institute of Certified Public Accountants (AICPA) called Statement on Auditing Standards No. 70, Service Organizations. This isn’t something you run yourself. You hire an independent accounting and auditing firm that performs the audit and issues a written report.

Actually there are two audits and reports. Type I is used to assess the suitability of controls that the organization has put into practice to achieve the security objectives. Type II includes that information, but is also a review of how effective the controls have operated during the time period being reviewed. That’s why Type II is so desirable. It shows that management has not only created a system but is actually performing to the procedures it has put in place.

What sort of things are audited? Important areas for the auditor include management and organization policies and procedures, physical security of the data center, logical security to ensure only authorized personnel have access to customer data, network security and management, application security and change control, system maintenance controls, incident reporting and resolution, change management, transaction processing, use of subcontractors and business continuity.

You can think of SAS 70 as something akin to the International Standards Organization ISO-9000 quality management standards and auditing for manufacturing organizations. They’re not the same thing, but both have the goal of providing assurance that you are dealing with a company that has effective processes and procedures in place and follows them. The principle is that sloppy seat-of-the-pants operations tend to deliver results that are all over the map. Sometimes things work, sometimes they don’t. You are much better off with a provider that can produce the same results over and over reliably.

What you want in a data center or cloud service provider is an operation that is secure and reliable above all. You wouldn’t prop open the back door to your in-house data center and let anyone who wanted to wander around unsupervised. Likewise, you want the peace of mind that the colocation facility that houses your servers has them secured in locked racks or cages and that nobody who doesn’t belong there can get into the data center at all.

The same is true of the networks that transport packets in and out of your servers. Those connections and the data that traverses them need to be under strict control so that your systems and data cannot be accessed by anyone who doesn’t have your express approval. One advantage of moving to a colocation center is that you are literally within walking distance of your carrier and perhaps your cloud service provider. With all the connections in-house, there is less likelihood of service disruptions or outsiders being able to tap into your data stream.

Service reliability is important as well. Having the servers and appliances locked down is great, but they also have to be on-line 24/7 to fulfill their mission. That’s where backup electrical power, cooling and network connections help keep your applications running non-stop is so valuable. The availability of trained technicians nearby is a way to ensure that if something does go wrong, it gets immediate attention.

Are you interested in moving to a high quality colocation facility or cloud service provider? Many now offer SAS70 Type II certification, so be sure to ask for that assurance when evaluating vendors. Get pricing and location for colocation and cloud services using SAS70 Type II Data Centers.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Monday, May 23, 2011

Global Crossing Ups Ante On Network Security

What’s a major expense for organizations that nobody wants to talk about? Security breaches. It seems like every few days there’s another big splash in the news about user accounts and credit card numbers being compromised. There’s the direct cost of having to make up for losses, but there’s the larger cost of concerned customers abandoning or avoiding the company out of fear they’ll be the next victims.

Get managed security options for your company. Click for features and pricing.These are the security horror stories we hear about. What generally isn’t reported is the espionage and theft of intellectual property that goes on behind the scenes. Your competitive advantage can be neutralized in minutes when key trade secrets and client lists are downloaded by unethical competitors and professional thieves.

Most companies are more attuned to network security than ever before. But is it enough? Judging from breaking news stories and industry buzz, not hardly. This is why Global Crossing is expanding its portfolio of security solutions for enterprise customers.

Global Crossing is well known as a leading worldwide IP network provider serving 40% of the Fortune 500 and hundreds of carriers, mobile operators and Internet service providers. They have the resources and the reach to deal with threats on an international basis. They also have the need, as their customers are prime targets for nefarious activities.

Global Crossings expanded suite of network security measures now includes a new SIEM or Security Information and Event Management platform. This resides in the Global Crossing Security Operations Center (SOC) where a team of security professionals, analysts and engineers monitor and assess network security issues on a full time basis. The reports and analysis are delivered to the proprietary uCommand portal for each customer.

The suite of security features includes a firewall, intrusion prevention service, web content filtering, antivirus and antispam appliance provided by Fortinet. This is augmented by additional professional services that include security policy review and creation, penetration testing, vulnerability assessments, incident response and security assessment and audit.

This is a multi-pronged approach that starts with evaluation and design of policies, procedures and technical measures, continuously monitors for threats, automatically thwarts them in progress and reports the attacks, plus jumps into action to deal with new issues as they arise.

The challenge of network security is that it is a rapidly evolving field with highly motivated and increasingly sophisticated perpetrators pitted against equally motivated security professionals. The more valuable your assets and the more your company depends on network connections and an online presence, the greater the threat to your operations.

Are you feeling the need for improved network security? If you are beyond what out of the box antivirus programs can do for you, a managed security solution may be your most cost effective option. Whether you have a small retail store or a Fortune 500 corporation to secure, get pricing and features of managed network security options new. You’ll likely sleep a lot easier knowing that someone in the security center is watching out for your interests.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Thursday, June 17, 2010

EVPL Ethernet Virtual Private Line Service

You are probably familiar with private line services for business. A private line is one where you have exclusive use. An analog telephone line is a private line. So is a T1 voice or data line. Now there is something new is the mix. It’s the VPL or Virtual Private Line.

Ethernet Virtual Private Line Service. Click for inquiryTelephone lines weren’t always private. Remember the party line? Decades ago, several houses in a neighborhood would be connected to the same physical line. If you picked up your phone to make a call, you might hear one of your neighbors already engaged in conversation. In the pre-Twitter days, listening-in on other phone conversations was often a form of amusement.

That lack of privacy is long gone for telephones. But shared digital services exist today, especially with public access Internet. No, you can’t casually eavesdrop on your neighbors email or Web activities, but if some of the users start heavily downloading large files, your Internet service will slow down. There are also tools available that allow anyone to monitor everything going over a particular WiFi hotspot. The whole Internet is one big party line in the sense that you can’t be sure who’s monitoring the traffic and what they might be doing with information they skim.

It’s the security risk and the lack of consistent bandwidth that have driven businesses to private line service. T1 lines are private lines. They offer the advantages of rock solid 1.5 Mbps bandwidth and exclusive use of the line. The disadvantage is that you pay for that line even when traffic is light or non-existant.

Ethernet also offers a private line service called EPL. It works like T1 in that it is a physical line connection between you and your service provider. The difference is that the protocol is Ethernet and you can often get scalable bandwidth, typically 10 Mbps.

If you have a private line service, why would you want a virtual private line service? For one reason, you may want private lines running from your headquarters out to a number of branch offices. With dedicate private lines, you need separate physical circuits for each of these lines. You pay for the exclusive full time use of each circuit and there may or may not be enough pairs of wire into your headquarters office to give you the number of private lines you desire.

Ethernet Virtual Private Line service, EVPL, uses a single physical copper or fiber circuit to connect you to the service provider. Within that circuit are multiple EVCs or Ethernet Virtual Connection. This is not a party line arrangement. Each EVC carries its own traffic to and from another location without any cross-talk or interference from other EVCs.

The power of EVPL is not only that you only need one network interface at each of your facilities, including headquarters, but that those virtual connections can be extended to other cities or states over the provider’s MPLS core network. The MPLS is a cloud network that carries traffic for many users, but the integrity of each user’s virtual circuit is maintained from point to point regardless of distance.

EVPL is also a switched layer 2 service, which means that you can use it to extend your LAN network across town or across the country. It’s the simplest way to bridge multiple LANs when they are not located in the same facility.

Can EVPL service be of benefit for your organization? Find out with a quick inquiry about Ethernet Virtual Private Line service. Our expert Telarus consultants will be happy to get you price comparisons and service level agreements so you can make the best decision for your company.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Thursday, June 10, 2010

MPLS Networks In Demand And Competitive

What’s the hottest telecommunications service that you may be missing out on? It’s MPLS networks. They’ve become highly in-demand and the source of competition among competitive carriers. Here’s what you need to know and how you can check to see if an MPLS network can save your company money.

Check MPLS network pricing and availability at MPLS Networks Today.


What’s driving the proliferation of MPLS networks is that enterprise applications are becoming more sophisticated and more dependent on connectivity among multiple locations. There are big cost savings to be hand through network convergence, enterprise VoIP and mission critical processes running on high throughput server farms. But for these benefits to be realized, you need WAN connections that are a solid as your company LAN.

The Internet isn’t up to it. True, the worldwide connectivity of the public Internet is unmatched. But network performance leaves a lot to be desired. Security is certainly an issue. Look at the efforts you need to put up to prevent your systems being infected by malicious bots and viruses. Beyond that, there is no promise of predictable performance. Bandwidth, path congestion, latency, jitter, corrupted and dropped packets are all up for grabs. That’s the reason TCP/IP was chosen as a data transfer protocol in the first place. If a packet doesn’t succeed at traversing the Internet at first, simply try, try again.

Such inconsistency can be tolerated for Web pages, email and many data transfers. Even the security issue can be managed with encryption. But time sensitive applications like real-time voice and video need better treatment. Who wants to get off the public switched telephone network and risk garbled and dropped phone calls? Could any call center survive with those problems?

The need for controlled and predictable network performance is what promoted the growth of private network solutions, such as Frame Relay. But Frame Relay is a technology who’s time has come and gone. It’s too expensive and, for the most part, too low in bandwidth for today’s needs. What’s replacing Frame Relay is MPLS.

MPLS or Multi-Protocol Label Switching networks are privately run networks that only serve their customer’s needs. Those needs typically demand secure point to point and multipoint connections with Class of Service (CoS) to make sure voice, video and data all have the network resources they need. Latency, jitter and packet loss are minimized. Bandwidth is sufficient to support all network requirements. If more customers come onboard, more resources are deployed to ensure quality performance for everyone.

MPLS services can be configured as point to point or fully meshed any-to-any connectivity. You specify how you want to connect and your service provider sets it up. New locations are easy to add or change. That makes MPLS networking an excellent option for businesses with many branch offices or retail locations. Two-way VSAT satellite has been the private networking solution for many retail stores, restaurants, gas stations and so on. But satellite bandwidth is limited, sometimes lost during heavy weather, and the cost isn’t necessarily cheap. It’s time to take a look at MPLS to see if this option makes more sense going forward.

MPLS Networks Today is a new service that makes it easy to get consultation and pricing for your multi-location network needs. With a quick inquiry, you’ll be connected to a team of expert consultants who have access to many MPLS service providers and access networks. Competition among IP network carriers with national and international service footprints has become intense. That means you’ll get highly competitive quotes that may be much lower than what you think this type of service will cost. Even if you aren’t currently in the market to upgrade your existing network, it could be well worth your while to check MPLS network pricing and availability. There’s a good chance you could be saving money with an MPLS solution.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Tuesday, March 23, 2010

PAETEC Adds Intrusion Detection For MPLS Networking

MPLS networks are on the ascendant as the preferred solution for linking multiple business locations. Now PAETEC is offering a new service to further enhance the security of its already secure MPLS network solutions by monitoring for network intrusions. What distinguishes this service is that operation and management is largely transparent to users.

Network intrusion detection and prevention keep your MPLS network secure.Network security has become a hot topic in recent years. We’re all familiar with the constant barrage of viruses, phishing schemes, hacking and other criminal activities on the Internet. You don’t need a connection to the Internet to worry about electronic security. Any company or organization with a computer network is a target for those who think they can benefit from compromising it. No amount of physical security protects your network once it leaves your premises. But to do business today, you need connections to multiple office locations, factories, warehouses, customers and suppliers.

This is where PAETEC, a telecommunications company with a nationwide fiber optic footprint, steps in. Rather than trying to build a meshed network from dedicated point to point lines and then having to install and manage network security appliances and software, you can simply turn the job over to PAETEC. They provide each of your locations with access to their privately-run network cloud. You define how you want each location to communicate. Built-into the network is the new managed Network Intrusion Detection and Prevention System known as IDPS. You don’t need to buy any special on-site equipment or install and maintain any network security software. It’s all built into the PAETEC MPLS network.

How does this system work? It’s a network based firewall with two components. The intrusion detection part inspects all traffic entering and leaving the network to identify suspicious patterns. It notifies the enterprise system administrator with recommendations on how to respond to any threat it finds. The second part is an intrusion prevention system that looks for potential threats and makes recommendations on how to respond before an actual break-in occurs. PAETEC operates a 24/7 Security Operations Center that can handle alarm responses for customers who don’t have their own full time system administrators.

The addition of an IDPS to your WAN network is more than just a good idea. It’s a requirement for sensitive applications such as PCI for credit card transactions and HIPPA for medical records. Health care modernization initiatives are certain to increase the number of locations connected by high speed MPLS networks and in need of industry mandated security.

Are you interested in starting a secure multi-location WAN network or improving the security of the one you have now? Would you like to do that in a cost effective way? If so, you should take a look at the secure MPLS network options from PAETEC and other competitive network service providers.

Click to check pricing and features or get support from a Telarus product specialist.


Follow Telexplainer on Twitter

Tuesday, July 10, 2007

Unified Communications Merges Everything

Convergence is a trend in enterprise networks, often focused on migrating telephony to the corporate LAN using VoIP. But the ultimate goal of unified communications involves integrating all electronic communications. That encompasses wired telephony, voice messaging, video conferencing, data networking, network security, VPN and wireless access.

Interestingly, Cisco already has a platform that will do all of this and more for the smaller business. It's the Cisco Unified Communications 500 Series. The basic solution includes telephony support for 8 IP phones, 4 FXS analog phones and 4 FXO analog trunk lines, plus support for SIP trunking. It has integrated voicemail and an auto-attendant, making it a full-featured small office PBX phone system.

So far this sounds like a typical small office IP PBX system. But the 500 series platform goes further. The antenna implies wireless communications. In this case it's an 802.11b/g wireless access point that supports wireless LAN IP phones as well as wireless data devices.

Connection to the WAN or Wide Area Network gives you broadband Internet access with full security via a Cisco IOS Firewall that supports point to point VPNs. Use these Virtual Private Network connections to include home workers or employees operating remotely. You can also easily expand LAN access inside the office by adding a Cisco Catalyst Express 520 Switch with 8 additional ports of 10/100 Mbps PoE (Power over Ethernet). This switch comes configured to work immediately with the 500 series.

With this system, called the Cisco Smart Business Communications System, you have up to 16 computer workstations, IP security cameras, or IP phone sets, a data/voice wireless access point, secure WAN (broadband Internet) access, secure VPN communications to remote locations, an in-house telephone system that connects to the PSTN and supports FAX machines and other analog devices, plus simplified set-up and management built-in. It's a single box that supports the complete small office communications needs.


Follow Telexplainer on Twitter